Hunt faster than the attacker.
Find who's already in.Stop who's next.
Huntbase is an autonomous threat hunter. When a new threat is published, Scout checks months of history across the tools you already run and your endpoints, responds within the rules you set, and proves it's gone.
Where we are now
The clock starts when they get in.
MTTR is usually measured from the alert. For a quiet intrusion, the clock started weeks earlier, and nothing fired to say so.
If your team only looks when an alarm rings, nobody looks at all.
Attackers get in before the patch.
Estimated mean time to exploit in 2025. Exploitation now routinely comes before a fix is released.
One in three hears it from someone else.
Of organisations first learned of the breach from an outside party.
Mandiant M-Trends 2026, via SecurityWeek (opens in a new tab)
Patched isn’t proof you’re clean.
CISA warned that patching Cisco firewalls didn’t remove the FIRESTARTER backdoor already planted on them.
“Boards should have confidence that their organisation can detect and investigate emerging cyber threats, including activity that existing security alerts may miss.”
Where you want to be
You know who got in, you’ve stopped them, and you can prove it.
- Every new threat is checked against your past the day it’s published.
- If someone got in, you know where, when and how, and the response is already under way within your rules.
- You can prove the threat is gone, and the same attack can’t land twice.
- Your team sets the rules and reviews the outcomes. Scout writes the queries at midnight.
How Huntbase gets you there
How a hunt runs, from new intel to proof
Scout hunts back through your history, acts within the rules you set, and leaves evidence you can check at every step.
Look back
Find who's already in.
New advisory, IOC or CVE? Scout checks it against weeks to months of history in your SIEM, EDR, cloud and data lakes, and on each host through the endpoint agent. The answer comes with evidence: hosts, users and a timeline.
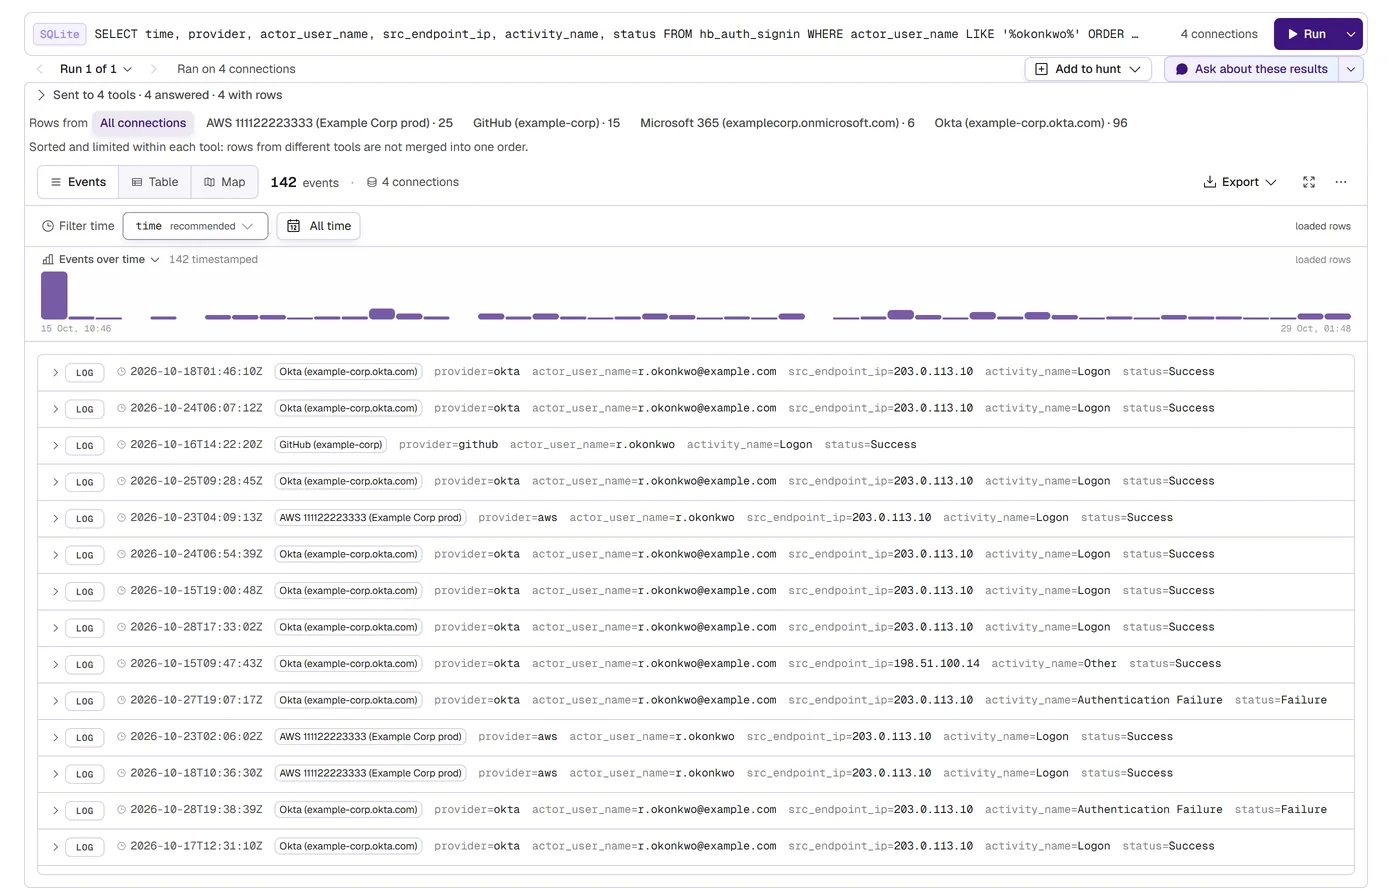
One question asked of four connected tools at once: 142 sign-in events, over time, in one list.
A patch closes the door. It doesn’t tell you who already walked through it.
Respond
Shut the door, proportionately.
Scout acts within your response rules: kill the process, quarantine the file, isolate the host only if the threat is still live. Anything outside your rules waits for a person, two by default. Every action can be undone.
Response · WKS-2231OperatorKilled process · quarantined file · WKS-2231
- Killed rundll32.exePID 4812
- Quarantined cache.dllC:\Users\Public
- Isolate host: not needed, threat no longer live
Rule: contain known-bad on workstationsUndoVerify
Prove it's gone.
Scout re-hunts to confirm the host is clean and records who acted, on whose behalf, and under which rule.
Verify · WKS-2231Re-huntRe-hunt clean
0 hits since containment · 3 sources checked
ActorScout on behalf of m.reyesRulecontain known-bad on workstationsRecorded14 Nov · 09:42 UTCKeep watching
Stop who's next.
The hunt becomes a watcher, backtested against 1,250+ attack recordings and run in shadow before it goes live. Scout also points out where you're exposed, so you can patch first.
Watcher · cache.dll side-loadStreamrundll32 loads an unsigned DLL from a public folder
- Backtested
- Shadow
- On
Backtested on 1,250+ attack recordings · 7 days in shadow
Patch first: 7-Zip 24.07 on 3 hostsCVE-2025-0411 · fixed in 24.09
What you want, and what you need
You want the answer. You’re accountable for the evidence.
Huntbase gives you both: the answer the day a threat is published, and the record behind it.
| Who | What they want | What they need |
|---|---|---|
| SOC and hunt leadsFor SOC teams | A calm answer when the CISO forwards the advisory. Fewer consoles. No lost weekend. | Evidence behind every answer, and every new threat in the news checked against their own history. |
| CISOsTrust center | To say “we checked” and mean it. | Proof for the board, auditors and regulators: what was checked, what was found, and which person or rule allowed each action. |
| MSSPs and IR firmsFor MSSPs | To serve more clients with the same team. | A defensible record of every hunt and action, kept separately for each client. |
Alongside the tools you run
They triage alerts.
Huntbase hunts.
Huntbase answers the questions nothing fired for. Keep the tools you trust: Huntbase reads their data and hands the evidence back as a hunt report, an export or over the API.
Your SIEM
Holds what was logged.Your EDR
Works what fired on the endpoint.Your AI SOC
Triages the alerts that fire.Huntbase
Hunts for what already got in, and stops it coming back.
A few of the 158 products Huntbase integrates with.

True today
Open, in use, and built by people who have worked the breach.
documented integrations
open hunt playbooks on the Huntbase Hub
public attack recordings that watchers are tested against
autonomy levels (Guide, Collaborator, Operator), with every action audited and undoable
Your hunts stay portable: the hunt.md format is an open spec (opens in a new tab), and Huntbase speaks Sigma, OCSF, STIX/TAXII and CACAO. Browse the Hub (opens in a new tab). Scout doesn’t train shared models on your data.
Already in?
Find out today.
Sign up and watch Scout hunt a new threat through the sample workspace, or book a demo and bring the threat you need checked.
Sign up.
Run a guided hunt on the sample workspace. No connector needed.
Connect your own sources when you're ready.